
Questo è quello che aggiungi al carrello
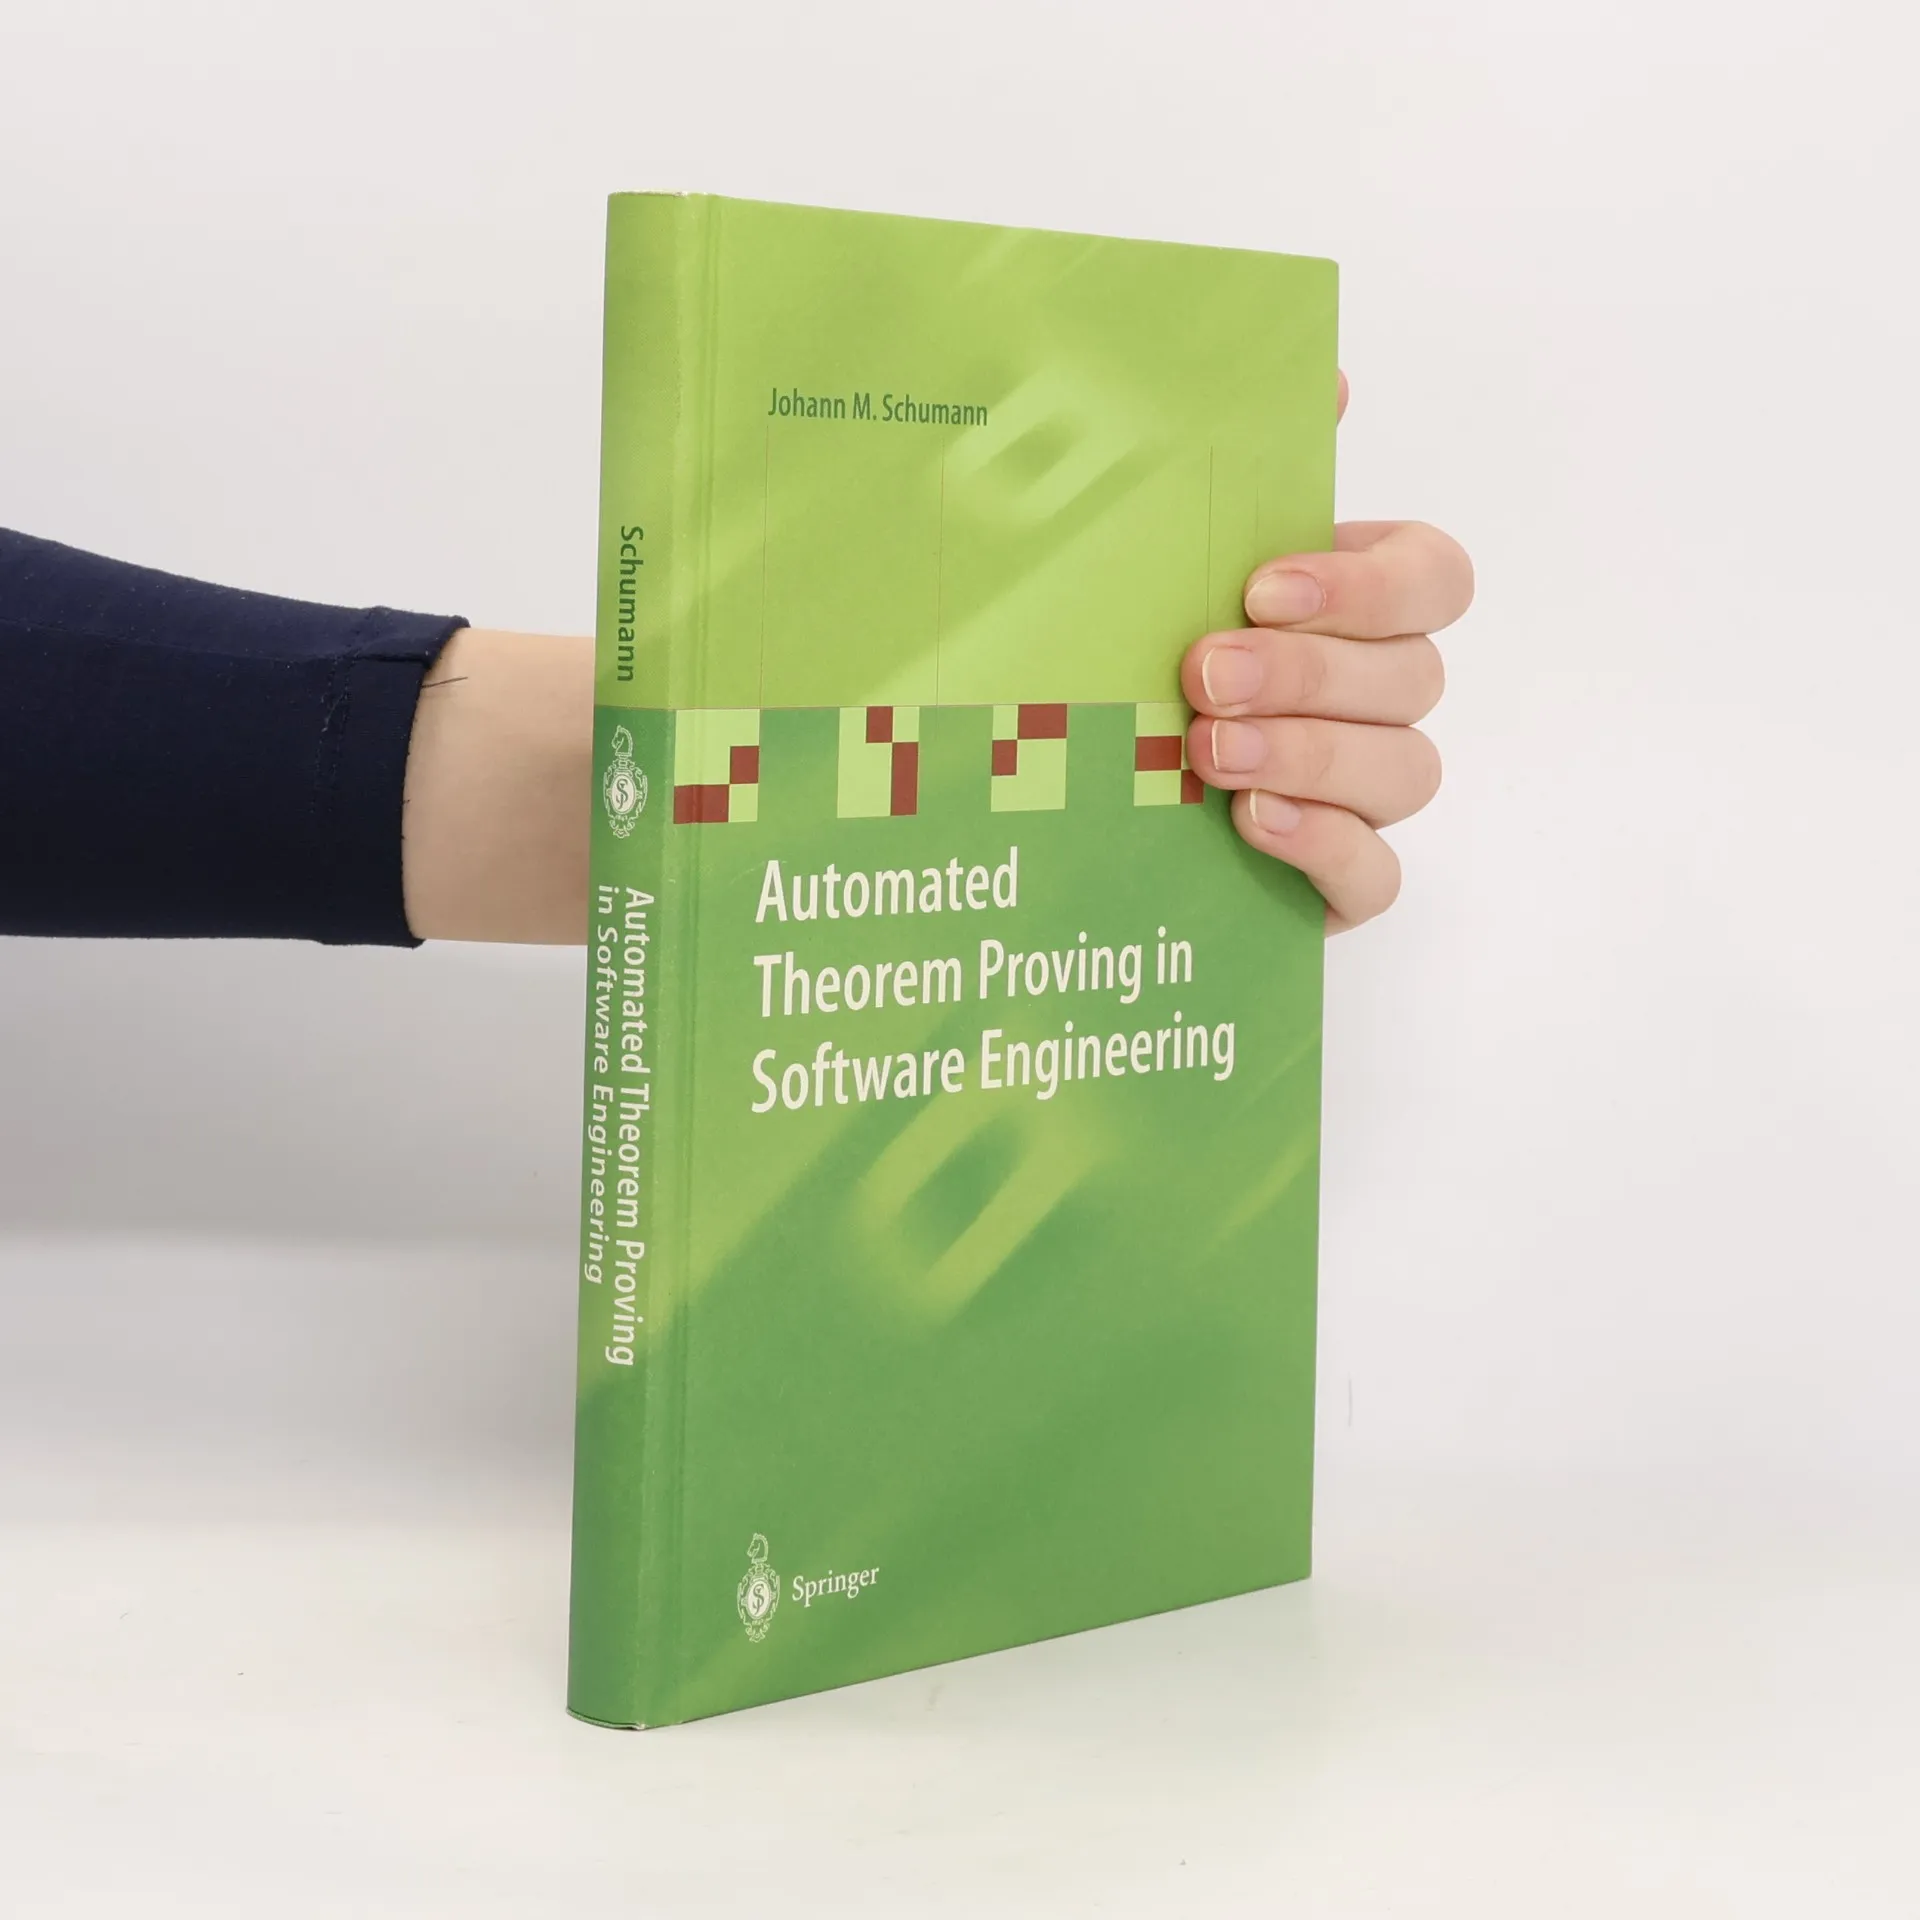
Automated Theorem Proving in Software Engineering
Parametri
- 228pagine
- 8 ore di lettura
Maggiori informazioni sul libro
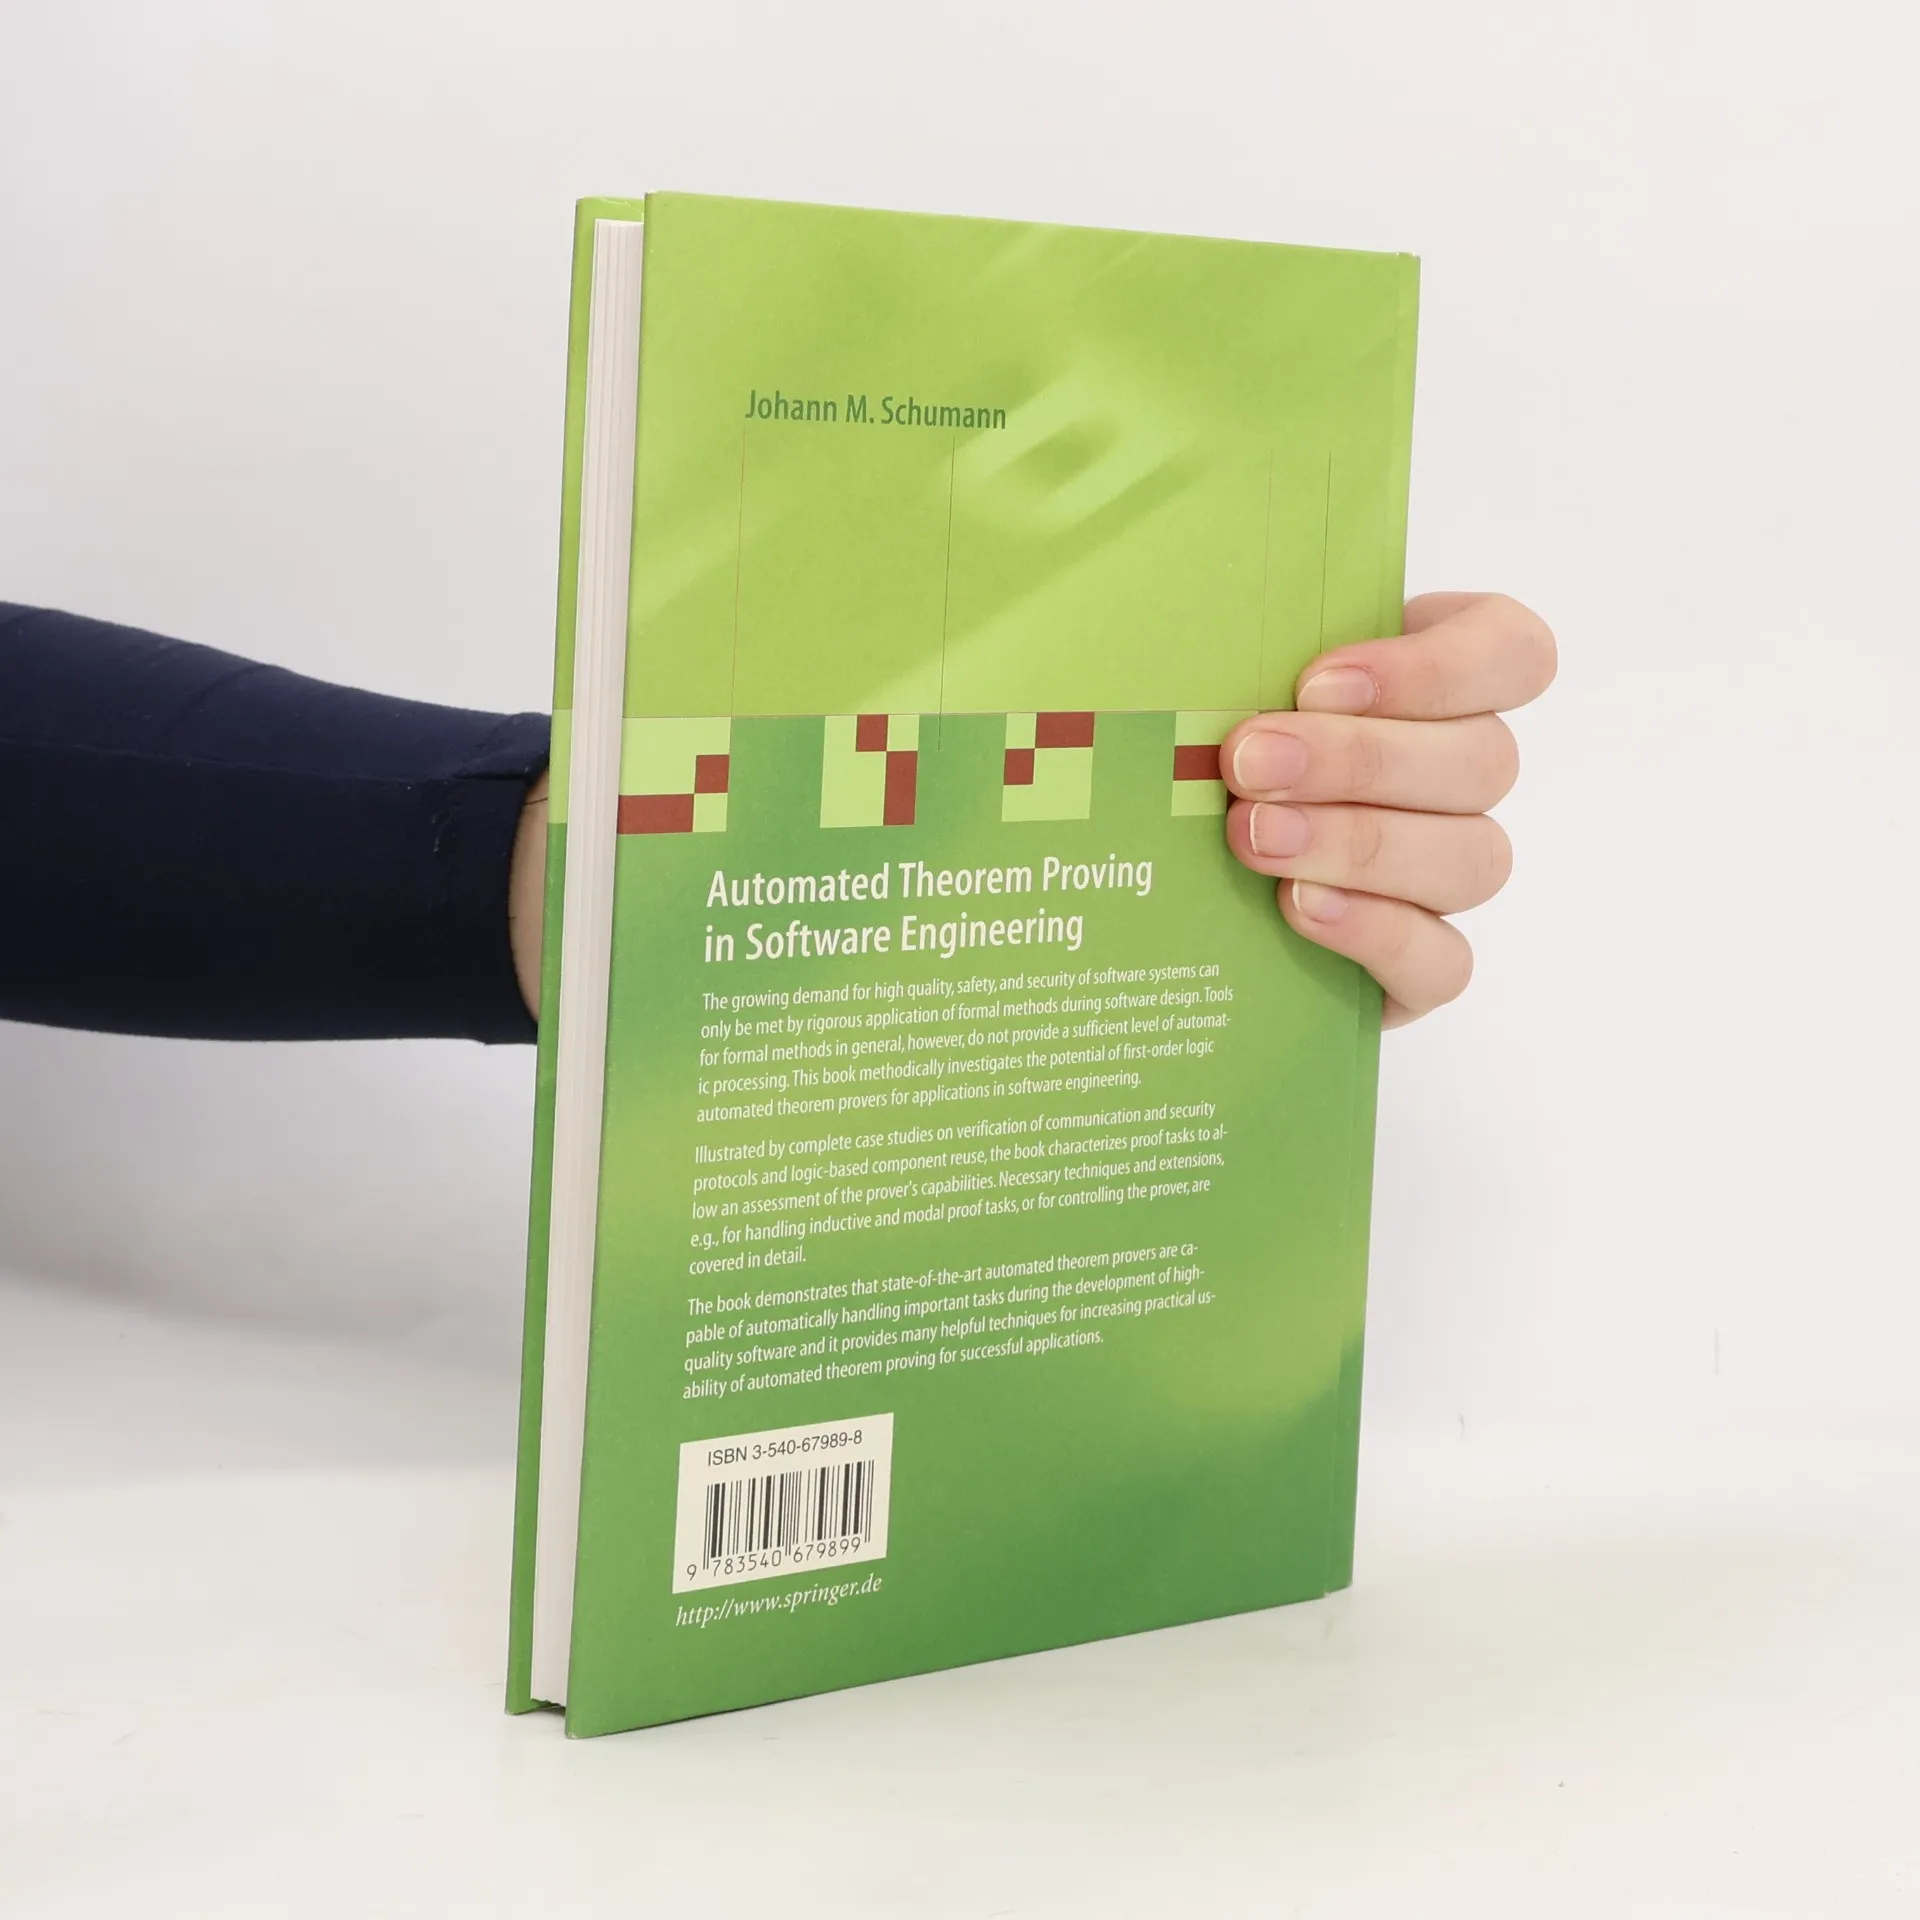
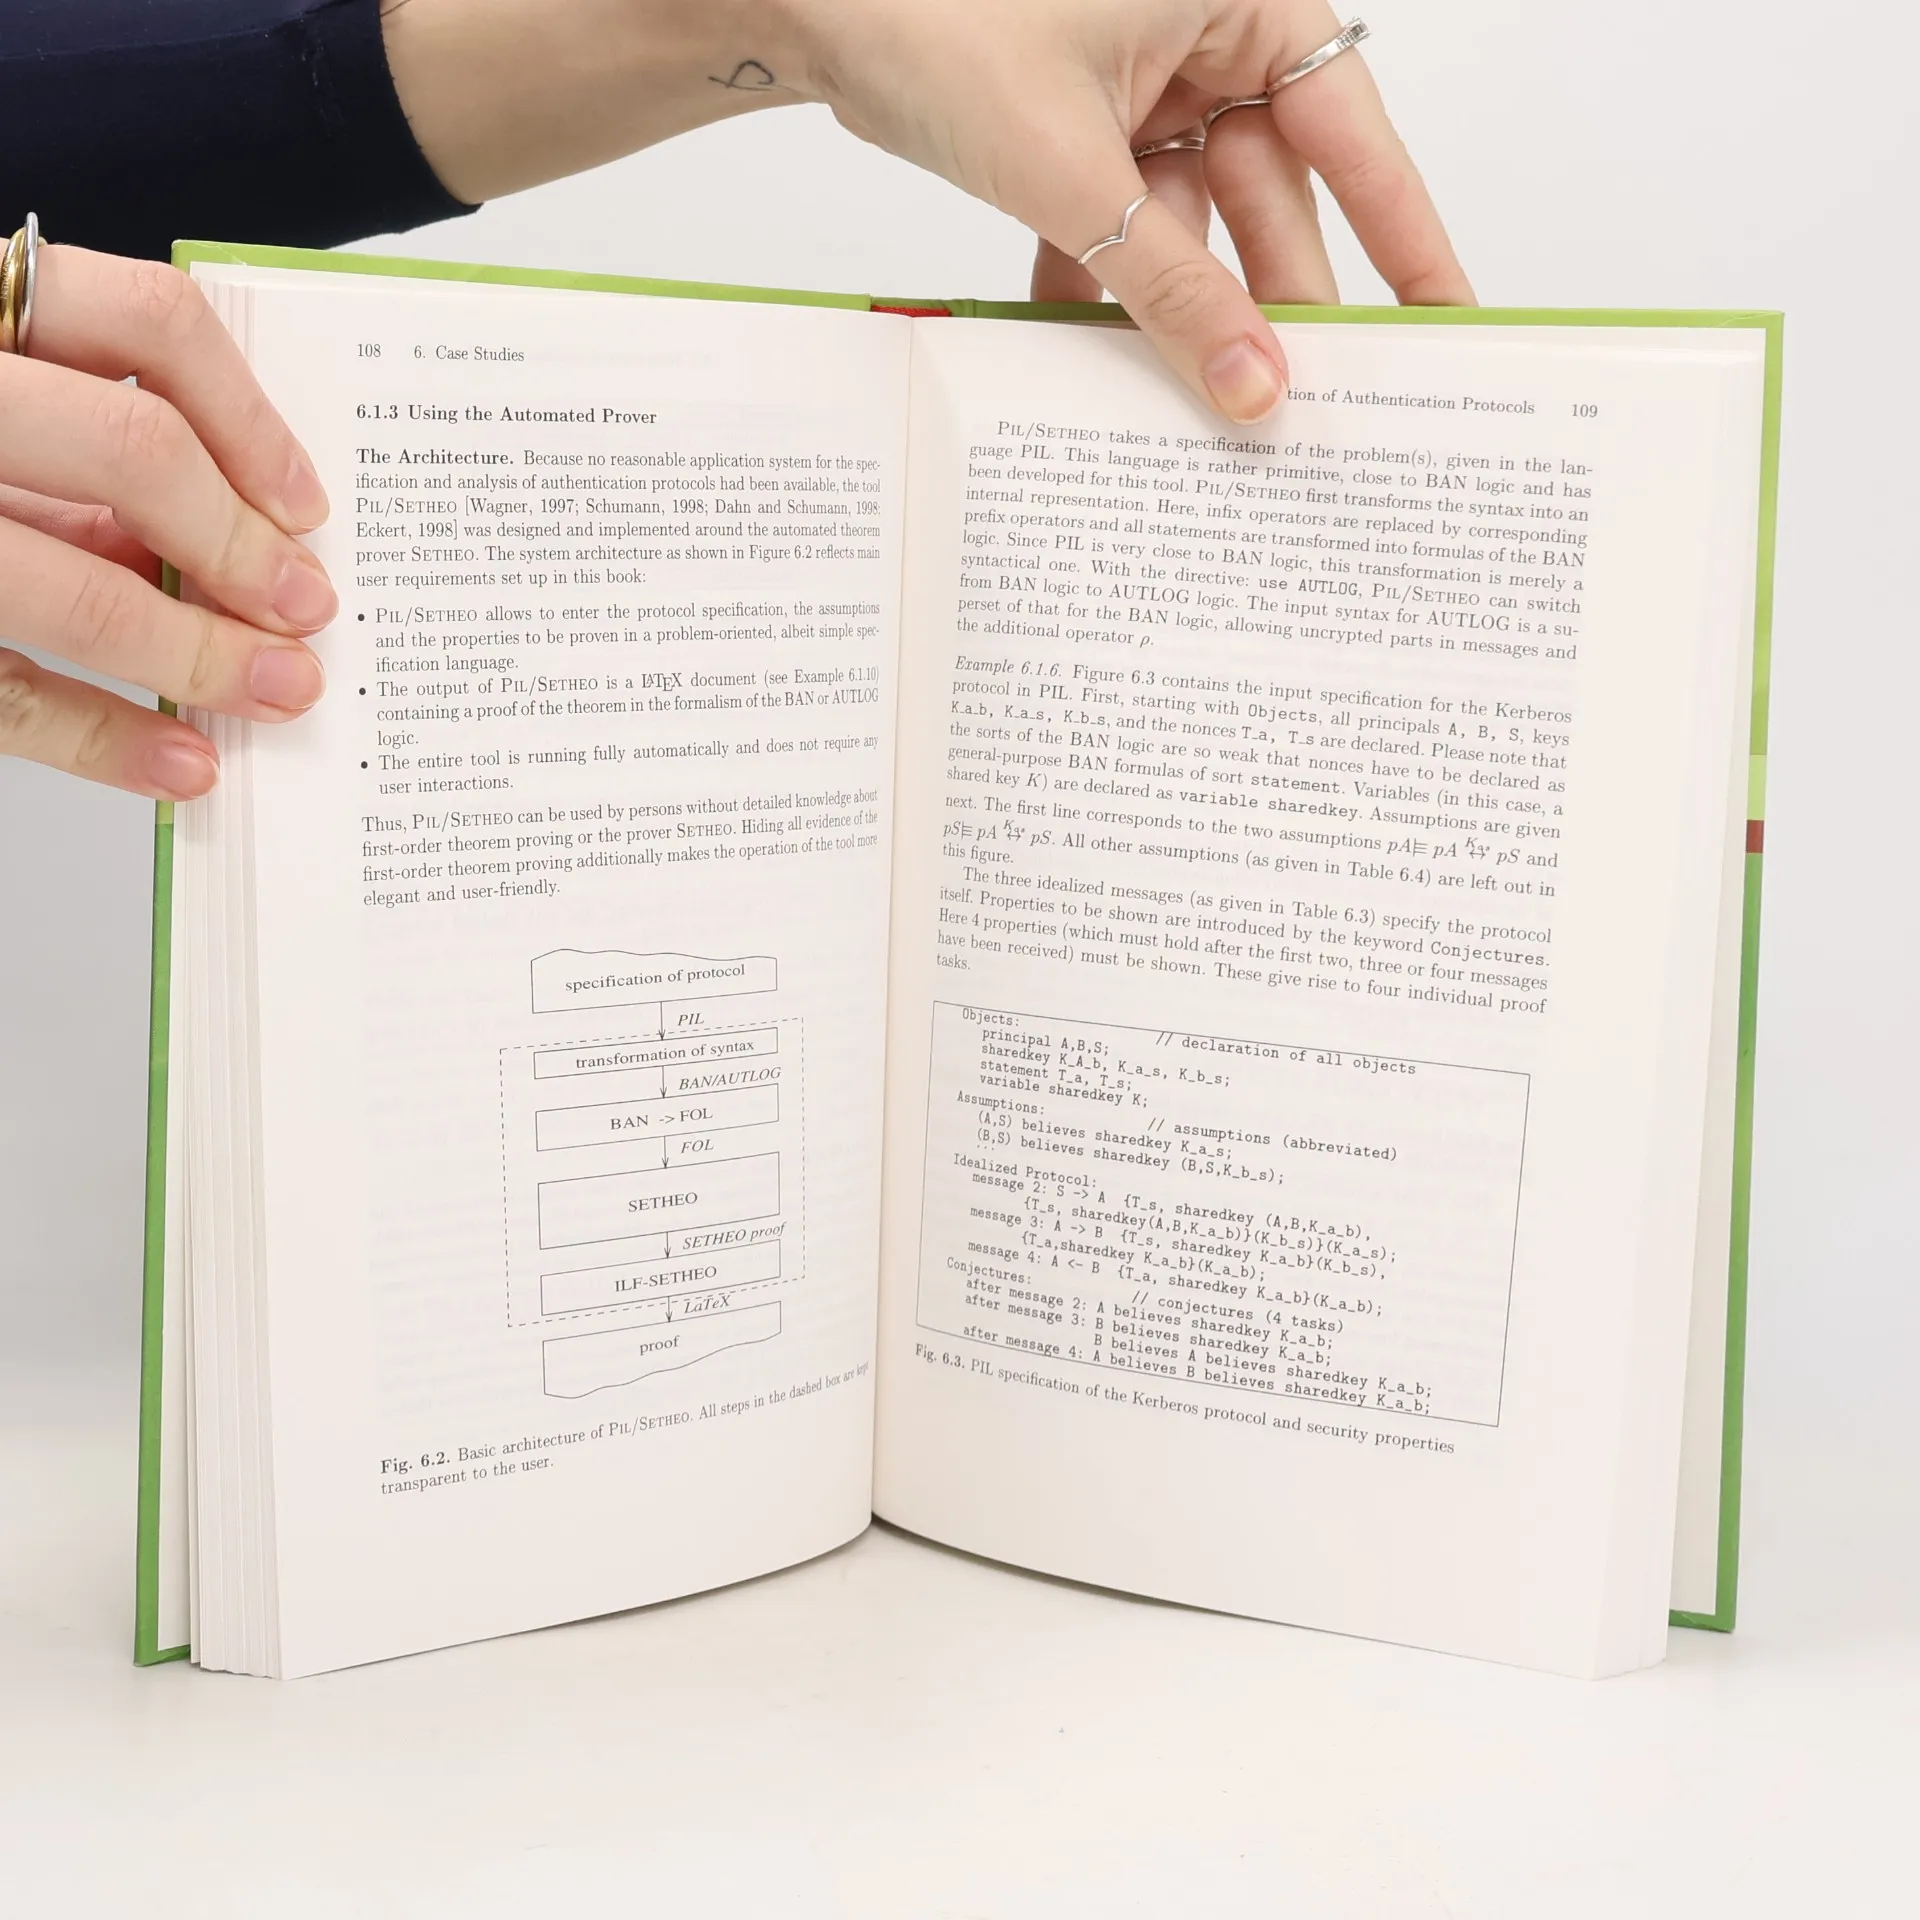
Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.
Acquisto del libro
Automated Theorem Proving in Software Engineering, D. Loveland, Johann M. Ph. Schumann
- Lingua

- Pubblicato
- 2001
- Rilegatura
- (Copertina rigida),
- Condizioni del libro
- In buone condizioni
- Prezzo
- 31,99 €
Metodi di pagamento
Ancora nessuna valutazione.
- Titolo
- Automated Theorem Proving in Software Engineering
- Lingua
- Inglese
- Editore
- Springer
- Pubblicato
- 2001
- Formato
- Copertina rigida
- Pagine
- 228
- ISBN10
- 3540679898
- ISBN13
- 9783540679899
- Serie
- Categoria
- Tag
- Architettura, Europa Occidentale, Intelligenza artificiale, Logica, Sistemi operativi, Sviluppo Software, Sistemi Informativi
- Descrizione
- Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.